| Piecemeal approaches | |
| “Some common issues we come across include a focus on end-point solution protection without any management or monitoring to ensure this is being kept up-to-date” |  Datapac : Karen O’Connor, general manager service delivery |
| Perhaps the most problematic issue we come across in taking over customer sites from an IT security perspective is that they have failed to employ a comprehensive IT security strategy that is appropriate to their site. What we often find is a piecemeal IT security approach that fails to adequately manage increasingly sophisticated cybercrime threats today.Some common issues we come across include a focus on end-point solution protection without any management or monitoring to ensure this is being kept up-to-date. This is something we see across many technology groups where an appropriate solution is deployed but not managed or maintained and this can be as dangerous as not having a solution in place due to the complacency it creates. Another common occurrence is a dependence on a single best-of-breed firewall which results in a single point of failure or target for attack rather than a tiered firewalling strategy. This is often for fear of administrative overhead however this is where a managed services provider can add value.
Many emerging trends such as mobility have created new IT security demands, however many organisations have omitted to factor this in to their security plans. A focus on on-premise device protection still seems to be predominant however a robust mobile device management policy is essential. In particular attention to data protection risks need to be addressed and fundamentals such as laptop encryption, application control on mobile phones and the securing of remote connections with two factor authentication are all vital. Another area often forgotten is network access. How are organisations protected from unapproved users and third parties plugging to their network and infecting it? A simple network access control solution could address this, detecting unauthorised devices and isolating them yet this is still overlooked by many. 
At Datapac, our approach is to take the time to understand each individual business and pertinent risks, and to work with the organisation to plan, design, deliver and manage an appropriate IT security solution to meet their needs.
|
|
| Service chaining | |
| “Firewall vendors are evolving their appliances to better control the threat of malware from the Internet. This limits the ability for malware to communicate with C&C servers right at the edge of the network” | 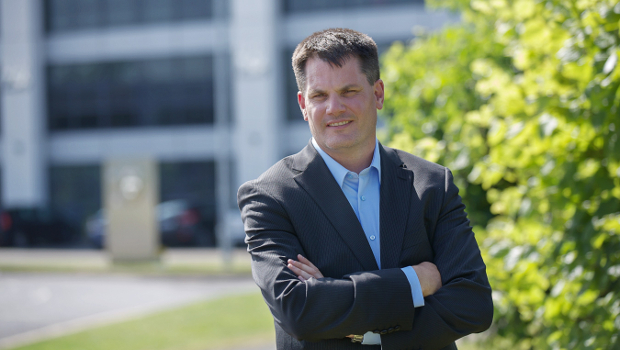 Agile Networks : Darragh Richardson |
| What a year 2014 has been for IT security. This year we have seen the multiple SSL vulnerabilities shaking the very foundation of what we use to secure transactions all over the Internet. Shellshock affected the bash shell on NIX systems and was quickly exploited to create botnets for DDos attacks.So what should organisations focus on to protect themselves moving forward? We can safely say that malware will continue to be a major source of data loss to organisations. Firewall vendors are now evolving their appliances to better control the threat of malware from the Internet. This limits the ability for malware to communicate with command and control (C&C) servers right at the edge of the network. Being able to track clients that are talking back to C&C servers is a first step for identifying malware. Organisations are also educating their employees on what to watch for and how to avoid being infected by malware. Users are still the main source of incidents in today’s organisations and with effective training an organisation can help reduce this exposure.
As organisations push further towards virtualisation the problems of virtual machine sprawl is becoming even greater. Organisations are putting effective controls and reporting in place to help manage the increased deployments of virtual machines. Without effective control of these deployments, it can lead to machines being deployed without proper security in place or being deployed in the wrong security zone leading to the machines being more vulnerable to attack. Customers start by taking applications like mail, CRM and ERP to the cloud initially. Architecture that supports strong encryption and effective two factor authentication is critical so that an organisations data remains and secure. Looking forward, organisations will start to move into more SDN-driven virtualisation and using overlay networks to connect and even extend their datacentres to public clouds. Here security becomes more essential than ever as the border of the datacentre now is very hard to define. Security is improved by using service chaining to force traffic through a security VM to be cleaned/scanned as it enters or exits the virtual estate. With service chaining an organisation can ensure that traffic is cleaned or stopped before it gets access to an organisation valuable data. Bring your own device (BYOD) also brings its challenges in securing the data on the device. Greater use of sandboxing and virtualisation on mobile devices is a way of controlling and securing data at rest on a device. Virtualisation techniques are being used to effectively dumb down the smart phone when accessing corporate data so that there is less chance of data being leaked to another application. One particular technique is the use of transparent virtual machines which allows a corporate application to be run in a virtual machine and because it is transparent the user does not have to open an interface first in order to launch the corporate application. Above all else smart organisations combine the best of internal and external expertise to find the balance between open, accessible networks which support end user needs and the appropriate security constraints to ensure that only the right people are accessing the right data from the right devices.
|
|
 Ltd