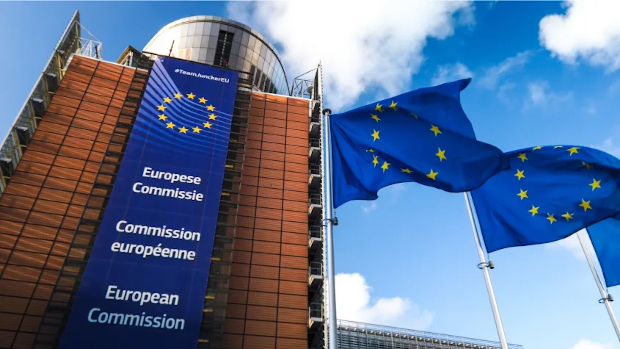
The European Commission is currently investigating a cyberattack that targeted its internal HR infrastructure. Although the identity of the perpetrators remains unknown, specialists from CERT-EU are working to establish whether confidential employee data has been stolen.
The attack primarily affected Sysper, the portal used to manage payroll, leave and professional development, as well as the Joint Sickness Insurance Scheme (JSIS). Although most staff experienced minimal disruption and Sysper is now back online, the JSIS platform remained offline for some time.
Security experts are particularly concerned about the potential leak of personally identifiable information, such as home addresses, contact numbers and salary levels. Although the HR platforms are isolated from the Commission’s main document servers, the theft of such data could enable highly targeted phishing or social engineering attacks against individual employees.
This incident follows a pattern of recent vulnerabilities, including a breach in January involving mobile device infrastructure and an incident in March in which almost 92GB of data was stolen from Europa.eu’s cloud systems.
Hacked in less than three hours
The rise in such attacks may be linked to the development of artificial intelligence in cyberwarfare. Tools such as Artex allow even non-experts to automate infiltration attempts. AI is used to work through different hacking techniques until a weakness is found, according to Sander Noels, who holds a PhD in AI safety and is the founder of cyber security company Enoki Labs.
According to the FBI, state-backed actors and criminals are already using these methods. In some cases, they gain full access to a system within three hours. Research from Stanford points to a dramatic leap in AI capabilities: models’ success rate on complex hacking tasks has risen from 15 per cent in 2024 to 93% in recent tests.
While major developers such as Anthropic are trying to restrict highly capable models because of safety risks, open source alternatives are rapidly closing the gap. Many ‘unfiltered’ AI models are available online free of charge or for a small fee, bypassing the ethical safeguards characteristic of mainstream software.
The danger is compounded by the speed at which attackers respond, says Noels. This year, software vulnerabilities have already been exploited on the very day they were discovered. This trend illustrates the urgent need for organisations to improve their defences to keep pace with AI-driven threats.
Business AM
 Ltd